 Governance and Policy Management
GRC that knows
your region.
60+ frameworks from the GCC, Africa, and international standards, in English, Arabic, and French. Hosted where your regulator says it should be.
Complyan AI does the busywork
It finds the tests a control needs, answers vendor security questions from the vendor's own documents, and cites where every answer came from.
Controls
Complyan AI found 6 tests relevant to this control.
Recommended tests for a control, added in one click.
Review in progress
Vendor security reviews answered, with the source cited.
Built for this region. Not adapted for it.
GCC and Africa frameworks, built in
UAE IA, SAMA, NCA, NDPA, POPIA, Kenya DPA, Ghana DPA, Egypt PDPL, CBN and more, alongside ISO 27001, SOC 2, and PCI DSS.
English, Arabic and French
The full platform in all three, RTL included. Your teams in Jordan, Lebanon, the GCC, and French-speaking Africa work in their own language.
Hosted where you need it
SaaS, on-premise, or private cloud across GCC and African regions. Your data stays in the jurisdiction your regulator expects.
Multi-entity, one account
Subsidiaries, departments, and tenants each keep their own posture. Group dashboards roll it all up for the board.
AI across every module
Control forms, policy drafts, risk updates, and vendor answers, each with the source cited so auditors can check the work.
The full compliance stack
Privacy, cyber risk quantification, AI governance, third-party risk, and audit management. One platform, one control set.
We answer to SAMA and the NCA, and for years my team proved the same control twice in two formats. With Complyan the evidence goes in once and both frameworks see it. Audit season is now a routine, not a fire drill.
Real screens from the product
Integrations, live monitoring, and third-party risk as your team will use them.
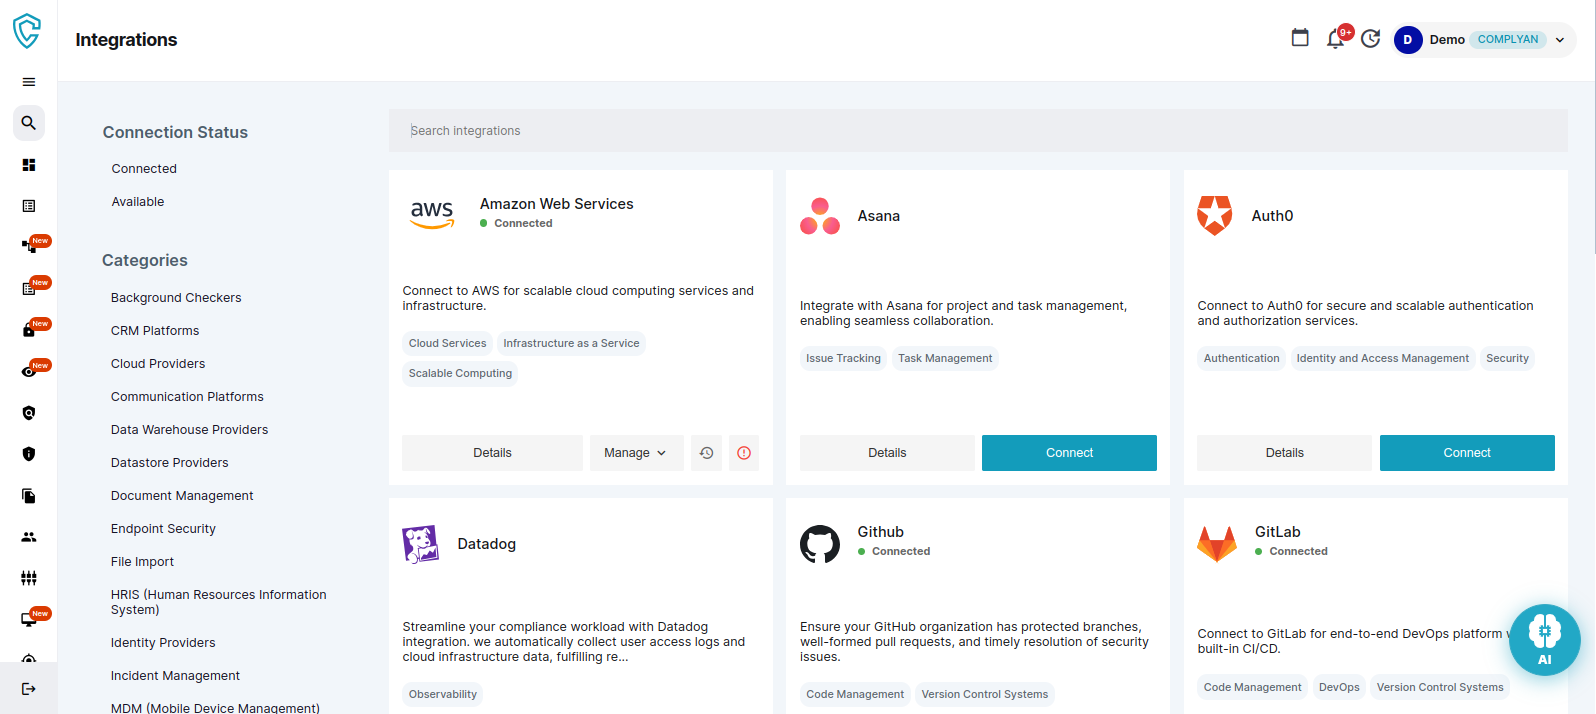
Your stack, connected
Connect AWS, Azure, GitHub, GitLab, Tenable, Okta, Datadog, and more. Every connection generates test cases mapped straight to your controls.
- Grouped by cloud, security, HRIS, and CRM
- Tests created automatically against relevant controls
- AES-256 encryption on every connection
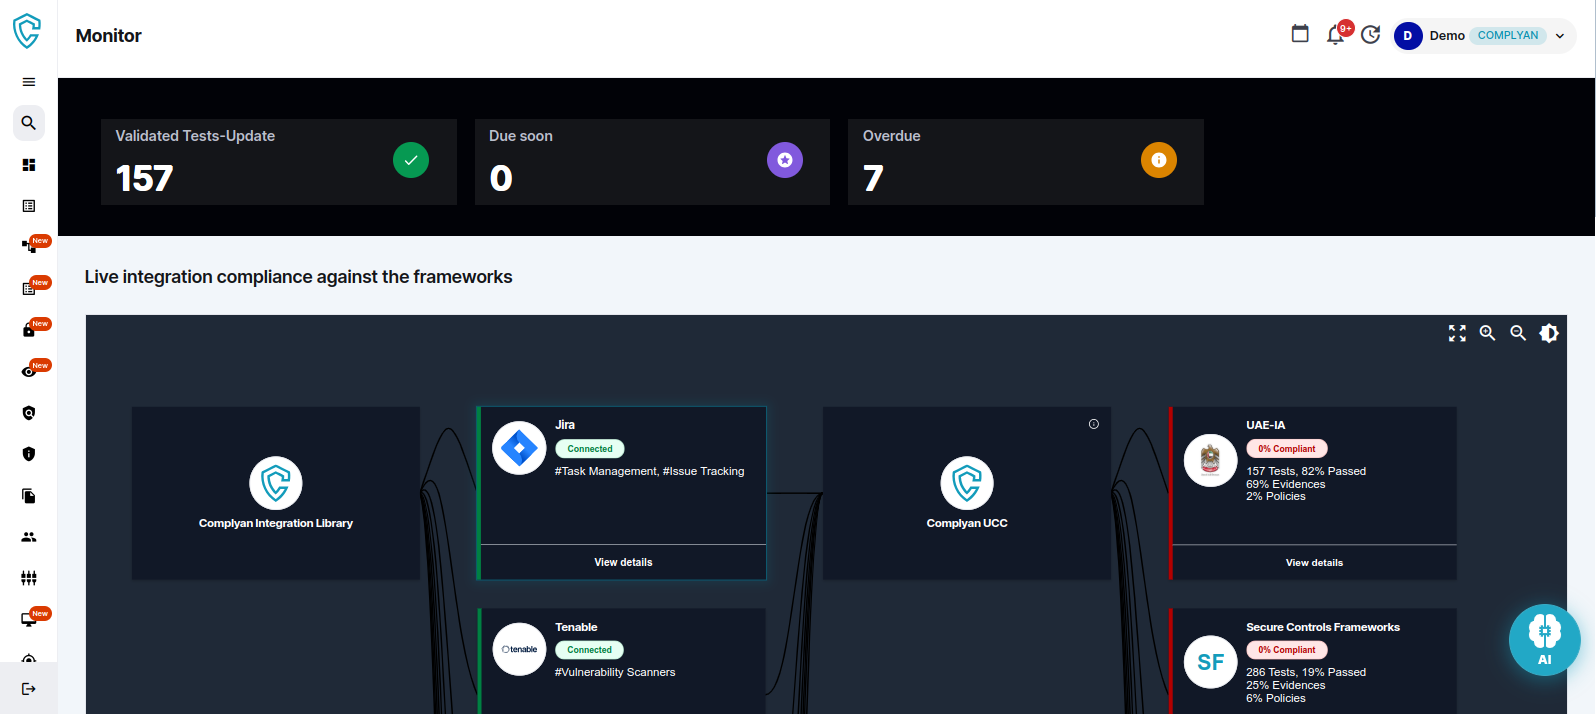
Compliance that updates itself
The monitor shows live compliance against each framework you subscribe to. When integrations run their tests, the numbers move. No spreadsheets to refresh.
- Validated, due-soon, and overdue tests in one view
- Status per framework, domain, and control
- Evidence ready for internal and external audit
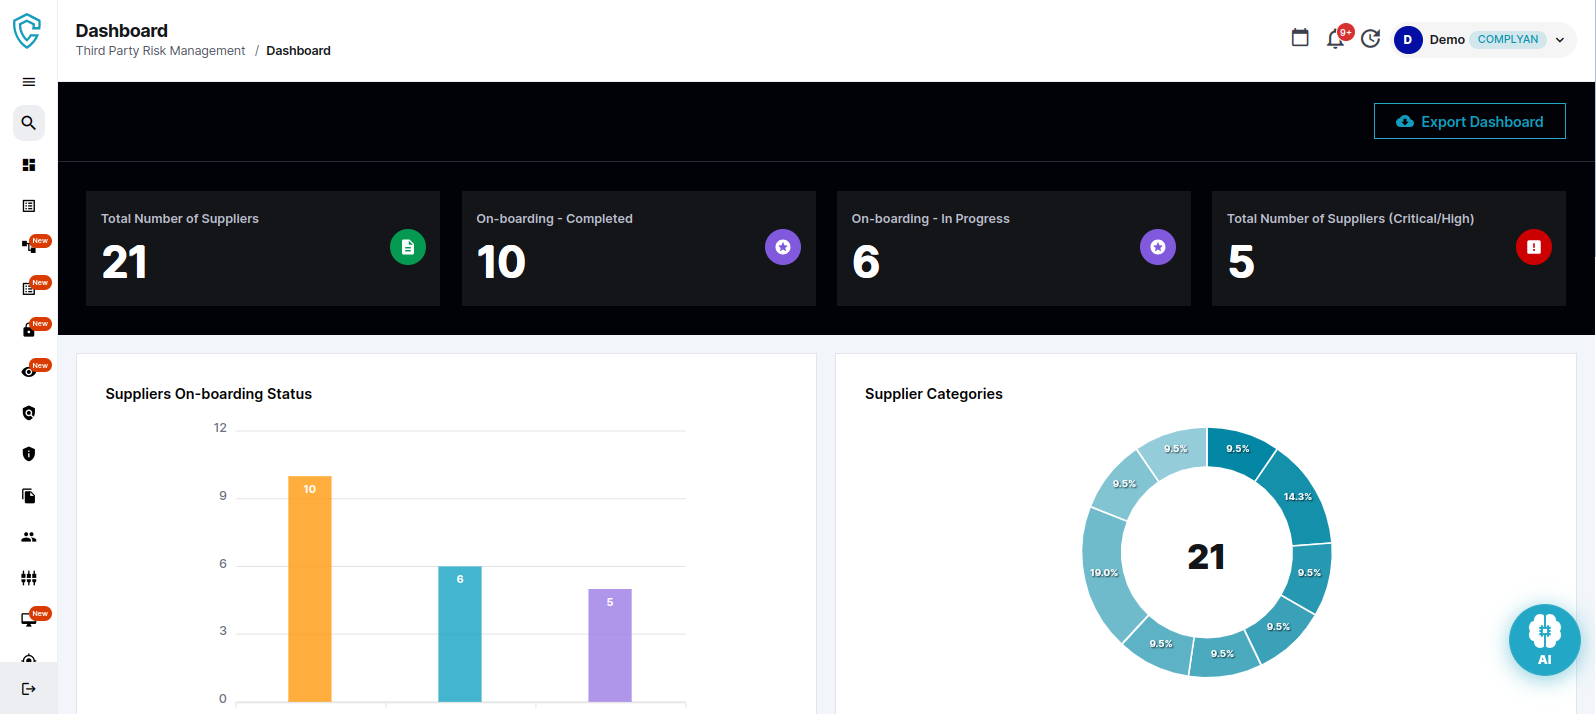
Every supplier, in one place
Onboard suppliers in bulk, send questionnaires, and track who is done, who is late, and who is critical across your whole vendor base.
- Bulk invites and questionnaire dispatch
- Onboarding status and category breakdown
- Exportable for board and governance reviews
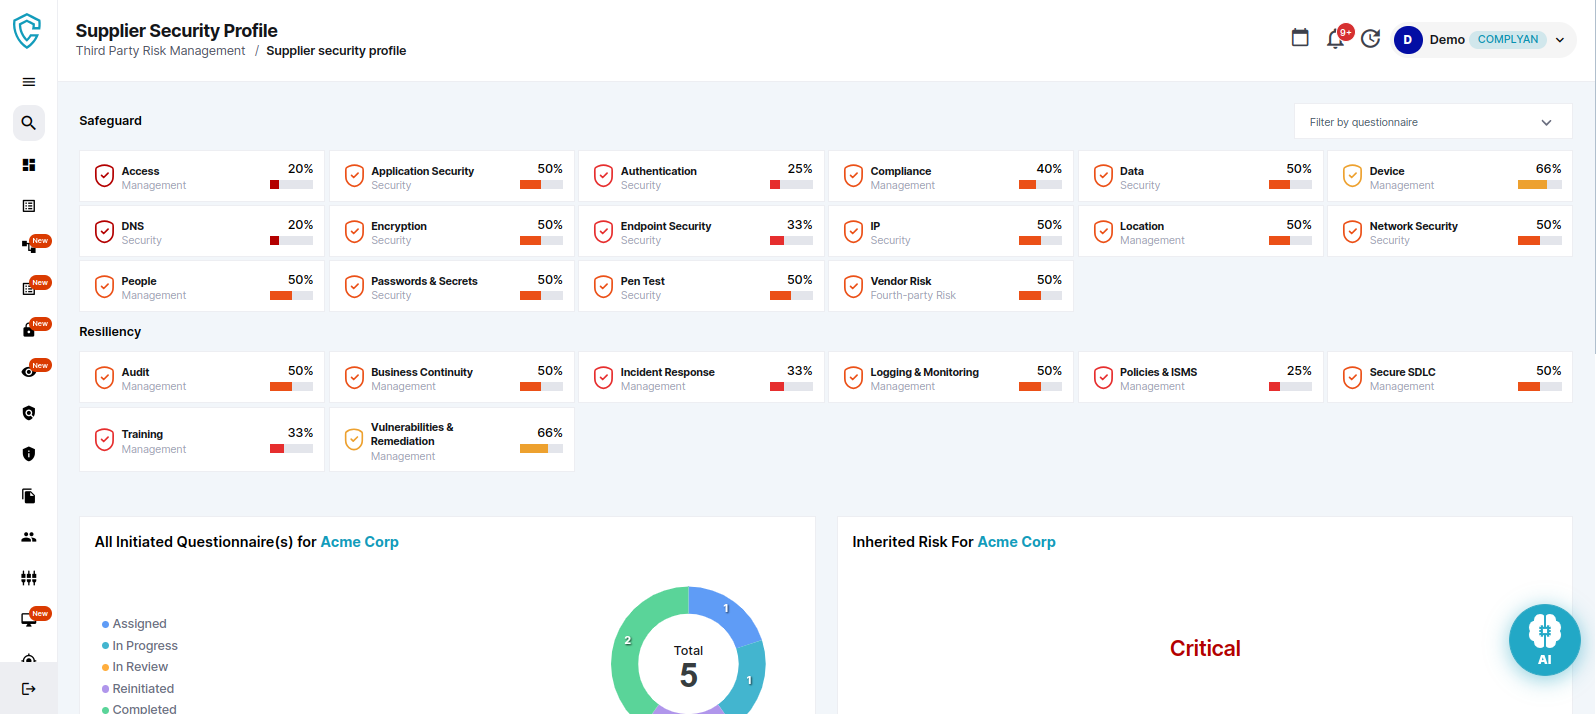
Scored across every safeguard domain
Each supplier gets a security profile scored on access, encryption, pen testing, incident response, and more, with inherited risk worked out for you.
- Safeguard and resiliency domain scores
- Questionnaire status per supplier
- Inherited risk from critical to low
Guides for the regulators you answer to
Written by our team for compliance leads, not consultants.
Saudi Arabia
NCA, SAMA and SDAIA
ECC, CSCC, NCNICC-1:2025, and AI governance for in-scope Saudi organisations.
Read the guides →UAE
UAE cyber regulations
UAE IA, VARA for virtual asset firms, and federal data protection requirements.
Read the guides →Kuwait
NBCC and CITRA DPPR
The new cybersecurity baseline and the 24-hour breach rules for telecom and IT licensees.
Read the guides →Nigeria
NDPA and CBN
NDPA 2023 obligations and the CBN data localisation directive for banks and fintechs.
Read the guides →Data protection
Privacy laws
PDPL, NDPA, and data sovereignty across GCC and African markets.
Read the guides →International
SOC 2
Type I versus Type II, and how to pick the report your customers will ask for.
Read the guides →Payments
PCI DSS
Cardholder data requirements for online retailers and payment businesses.
Read the guides →Multi-framework
Cross mapping
Common control frameworks and how to stop doing the same audit work twice.
Read the guides →Where we operate
Pick a region, then open a country to see its frameworks.
- UAE IA
- UAE PDPL
- DIFC and ADGM data protection
- DISR (Dubai)
- ADHICS (Abu Dhabi health)
- NCEMA 7000
- VARA
- NCA ECC
- NCA CCC and CSCC
- NCNICC-1:2025
- SAMA Cybersecurity Framework
- CMA
- PDPL
- CBK
- NBCC baseline
- CITRA Data Privacy Protection Regulation
- CITRA IT governance
- CBB Rulebook
- Bahrain NCSC baseline
- Bahrain PDPL
- QCB
- Qatar NIA
- Qatar PDPL
- CBJ
- Jordan Personal Data Protection Law
- CBO
- Oman Personal Data Protection Law
- NDPA 2023
- CBN Risk-Based Cybersecurity Framework
- CBN data localisation directive
- Ghana DPA
- Bank of Ghana cyber and information security directive
- POPIA
- Joint Standard on cybersecurity (FSCA and PA)
- Kenya DPA
- CBK cybersecurity guidance
International standards on the same engine
Complete a control once and Complyan credits it across every framework that shares it, regional or international.
- ISO 27001:2022
- ISO 27701
- ISO 22301
- ISO 20000-1
- SOC 2
- NIST CSF 2.0
- PCI DSS
- GDPR
- DORA
- HIPAA
- COBIT
- SCF
Common questions
NCA ECC, CCC, CSCC and NCNICC-1:2025, SAMA, CMA, UAE IA, UAE PDPL, DISR, ADHICS, NCEMA 7000, QCB, Qatar NIA, CBB, CBK, NBCC, CBO, and CBJ, among others. Each ships with its own control library, not a copy of a global template.
POPIA in South Africa, NDPA and the CBN frameworks in Nigeria, Kenya DPA, Ghana DPA, and Egypt PDPL. See our NDPA 2023 guide for how this works in practice.
Yes. SaaS, on-premise, and private cloud are all supported across GCC and African regions, so you can meet NCA, UAE IA, or CBN data localisation requirements.
The full platform. Forms, dashboards, reports, and policies render in the chosen language, with RTL layout for Arabic.
Complyan uses the Secure Controls Framework as its mapping backbone. Complete a control under one framework and every equivalent control in your other frameworks is credited. More in our cross mapping guide.
From your own documents and, for vendor reviews, the vendor's own reports. Every answer shows its source. Read how we handle your data in Security for Complyan AI.
Yes. Each entity or tenant keeps its own frameworks, posture, and dashboards, and group reporting rolls up across all of them.
Global tools are built around North American and European rules and add the region later. Complyan started with the GCC and Africa: native frameworks, real Arabic and French support, and in-region hosting.