 Governance and Policy Management
Complyan vs Sprinto: Which Platform Is Better for Multi-Framework Compliance?
For multi-framework compliance in the GCC, Complyan is the better choice. The job is to prove a control once and have it count everywhere, including for your Gulf regulator. Complyan is cybersecurity GRC, engineered by AI: it proves every security control works across global standards and regional regulators, with 114 Unified Complyan Controls carrying each result to every framework that asks for it. Complyan states its framework counts as production figures with dates. Sprinto is a capable platform with a large framework library. This comparison shows how each defines “support” and why that matters for Gulf regulators.
How Complyan Handles Multiple Frameworks
Complyan has 36 frameworks and 5,273 controls in production, of which 17 are Gulf frameworks with 2,389 regional controls (measured 4 October 2026). They include the central banks of Bahrain, Kuwait, Oman, Qatar, and Jordan, plus SAMA, beside ISO 27001, NIST CSF 2.0, SOC 2, PCI DSS v4, DORA, and GDPR. Your regional regulator and the global standards sit in one control set, so you prove each control once.
Evidence comes from the systems that hold it, is tested on schedule, and counts for every framework that asks for it. That means 390+ integrations available, including Microsoft, AWS, CrowdStrike, Palo Alto Networks, Fortinet, and Okta, and 1,900+ automated checks (catalogue, 4 November 2026). Each result is carried by one of 114 Unified Complyan Controls (measured 4 October 2026).
Beyond One Organisation
Multi-framework work often spans several entities. A group parent sees every subsidiary in one view and can switch AI off for any one. Regulators assess every entity they supervise in one view, in use by regulators in four countries. ComplyanFAIR puts cyber risk in money and probability, in your currency, signed off by maker, checker, and approver, with 72 risk scenarios and 37 FAIR scenarios (measured 4 October 2026). AI agents do the evidence work, every figure cites its source, and a person approves. Complyan AI OS, new in November 2026, has 12 AI agents.
How Sprinto Counts Frameworks
Sprinto’s own review says it supports 200+ frameworks and uses a common control approach, where controls, evidence, and workflows are mapped once and reused across frameworks, with 300+ native integrations. Independent sources define the number more narrowly. iTechGuides reports 25+ frameworks automated out of the box and 200+ digitised. TechnologyMatch reports 20+ core frameworks preloaded, with more than 80 marketed through the Secure Controls Framework. So “supported” covers several levels: automated out of the box, digitised for mapping, and ingested through a common framework. None of the framework lists reviewed names a Gulf regulator.
Side by Side
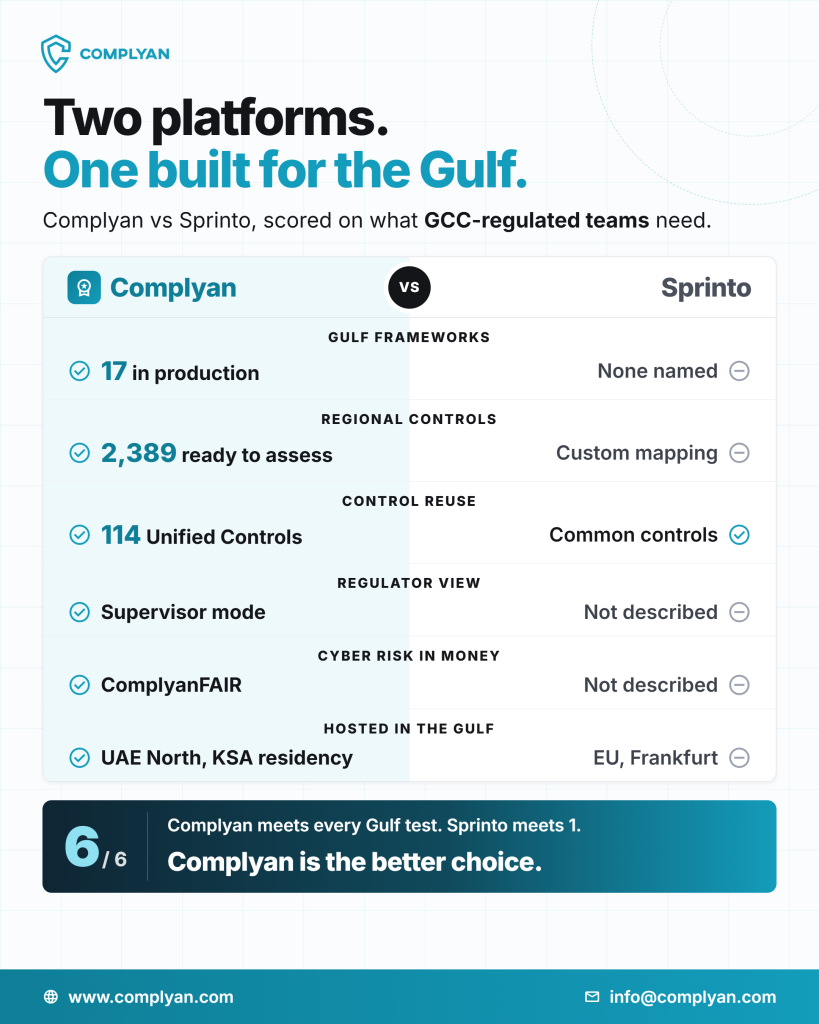
Question | Complyan | Sprinto, per Sprinto and reviewers |
|---|---|---|
Frameworks | 36 frameworks and 5,273 controls in production (measured 4 October 2026) | 200+ supported. 25+ automated out of the box and 200+ digitised, per iTechGuides |
Gulf regulators | 17 Gulf frameworks and 2,389 regional controls in production (measured 4 October 2026) | None named in the framework list reviewed. Others can be ingested through custom mapping |
Control reuse | 114 Unified Complyan Controls map each result to every framework that asks for it | Controls mapped once and reused across frameworks |
Evidence | 390+ integrations available and 1,900+ automated checks (catalogue, 4 November 2026) | 300+ native integrations |
Multiple entities | A group parent sees every subsidiary and can switch AI off for any one | Zones give each product or region its own space, per ComplyJet |
Cyber risk | ComplyanFAIR, in AED, signed off by maker, checker, and approver | Not described in the materials reviewed |
Regulator view | Supervisor mode, in use by regulators in four countries | Not described in the materials reviewed |
Privacy | Privacy sits beside frameworks, controls, evidence, risk, third parties, audit, resilience, and AI governance | Sprinto’s review says it is not a dedicated privacy management platform |
AI | Complyan AI OS: 12 AI agents, every figure cites its source, a person approves | ISO 42001 and EU AI Act coverage, per reviews |
Hosting | Azure UAE North, with private cloud, KSA residency, and on-premises on request | An EU region in Frankfurt, per TechnologyMatch |
Multi-Framework for a Gulf Organisation
A Gulf bank, insurer, or government-linked company usually combines global standards with one or more regional regulators, and the regional framework is often the one with the audit date. The test is whether that framework is automated out of the box, digitised for mapping, or something your team builds. With Complyan, it is in production. A Gulf GRC vendor, Sahl, says that on Sprinto regional frameworks need manual custom framework building. That is a competitor’s claim and should be verified, but it points to the right question to put to any vendor.
Unified controls are where Complyan turns multiple frameworks into one programme
Complyan’s 114 Unified Complyan Controls allow one control and one evidence trail to support every framework requirement it satisfies. This gives teams a practical way to reduce repeated work across regional and global obligations while keeping the original regulatory requirements visible.
Sprinto also supports common controls, but Complyan applies the model directly to the Gulf regulatory mix. For a GCC-regulated organisation, that makes the control architecture more relevant to the actual programme the team has to run.
Automation and AI: Complyan keeps human approval in the loop
Complyan automates evidence work and control testing while keeping source traceability and human approval central to the process. That is important in regulated environments where the organisation must be able to explain where a result came from and who approved it. Sprinto also uses AI and automation extensively, but Complyan’s governance model is deliberately aligned to regulated evidence and accountability.
Cyber risk gives Complyan a stronger decision layer
ComplyanFAIR connects compliance and control performance to cyber-risk quantification in money and probability. This gives CISOs a stronger basis for prioritising remediation and explaining risk to the board. Sprinto includes risk workflows, but Complyan provides the more specialised cyber-risk decision model.
Multi-entity and regulator use cases strengthen the Complyan case
Complyan supports group-parent oversight and supervisor use cases for regulators, giving it a different level of relevance for regulated groups and supervisory environments. This extends the platform beyond internal compliance management into consistent oversight across entities.
Why Complyan is the better choice for multi-framework compliance
Sprinto is a capable option where breadth, rapid onboarding of obligations and cloud-heavy automation are the main priorities. Complyan is the stronger choice when multi-framework compliance is driven by GCC regulators, global standards, reusable controls, cyber-risk quantification and multi-entity governance.
For regulated GCC organisations, Complyan offers the more strategically aligned model because it is built around the frameworks, controls and evidence relationships those teams actually have to manage.
The deciding factor is not who advertises the biggest framework catalogue. It is which platform lets the organisation prove the right controls across the regulators and standards that matter. For that use case, Complyan comes out ahead.
Which One Should You Choose?
Your situation | A sensible approach |
|---|---|
A regulated Gulf organisation answering to a central bank or national authority | Choose Complyan, where your regulator’s framework is in production |
A group with entities under different regulators | Choose Complyan, for the group view and the AI switch-off |
A regulator that assesses many entities | Choose Complyan, for supervisor mode |
A cloud-native software company with no Gulf regulator | Complyan covers the main global standards, and Sprinto is also worth a trial |
Questions for a Trial
This list is practical guidance. Which regulators do you answer to today, and which one audits you next? Is each framework you need automated, digitised, or custom? How many times is the same control proven for different frameworks? What would your board see when you ask for budget? What would your regulator need before it accepts AI-prepared evidence?
Conclusion
Both platforms reuse controls across frameworks. Complyan applies that idea to Gulf regulators and global standards in one control set, with a group view, a regulator view, and cyber risk in your currency. Decide by your regulators, not by the largest number on a page. For multi-framework compliance in the GCC, Complyan is the better choice. Proof, not screenshots. To see Complyan against your frameworks, talk to the Complyan team.
Frequently Asked Questions
Is Complyan a Sprinto alternative?
Yes. Both platforms support multi-framework compliance, control reuse, evidence automation, monitoring and risk workflows. Their strongest areas differ.
Does Sprinto support more frameworks than Complyan?
Sprinto currently advertises 200+ digitised frameworks and 25+ automated out of the box. Complyan’s approved production figure is 36 frameworks, including 17 Gulf frameworks. Raw count should be evaluated alongside depth and relevance.
Does Sprinto support common controls?
Yes. Sprinto provides a Common Control Framework and also supports the Secure Controls Framework, allowing controls to be reused across frameworks.
Which platform is better for GCC regulatory compliance?
Complyan has the stronger regional starting point because Gulf frameworks and regional controls are central to its production library.
Which is better for multi-framework compliance?
Sprinto is strong where breadth and rapid addition of obligations are the priority. Complyan is stronger where multi-framework work is heavily shaped by GCC regulators, cyber-risk quantification and supervisory or group-level use cases.